Before 100,000 Items: SharePoint Permissions for Irish SMEs
Manage SharePoint permissions for Irish small businesses: prefer groups, avoid item-level scopes, and prevent slowdowns before libraries reach 100,000...
Use groups and inheritance as your default, and only break inheritance when you genuinely need to. Prefer Microsoft 365 groups for team sites and SharePoint groups for communication sites, let permissions flow down from the site, and save custom access for the few cases that truly need it. Watch your unique permission counts and folder item limits so performance stays solid as your business grows.
TL;DR:
- Limiting the number of unique permission scopes is crucial for maintaining SharePoint performance, especially as libraries grow beyond 100,000 items.
- Using folder-level sharing reduces complexity, but extensive permission breaking or restoring across many items can cause management and speed issues.
- Managing permissions through Microsoft 365 groups on team sites helps keep access consistent across connected apps, while SharePoint groups suit communication sites with no Microsoft 365 backbone.
- Regular quarterly reviews of external links, guest accounts, and permission scopes prevent permission sprawl and ensure access remains appropriate.
- When in doubt, assign the lower permission level to users, as upgrading is easier than removing unnecessary access later.
Table of Contents
- SharePoint permission levels and groups: what each level and group does
- Permission inheritance and unique permissions: why limits matter and how to plan for them
- Step-by-step: grant, change or remove permissions in the SharePoint modern experience
- Permissions strategy and best practices tailored for small businesses
- Audit, review and remediation: a simple recurring process
- When to get help from hostme.ie and what we do
- Author perspective: practical trade-offs and a short checklist
- Quick hostme.ie contact and services links
- Sources
- FAQ
SharePoint permission levels and groups: what each level and group does
SharePoint permission levels tell you exactly what someone can do once they have access. Getting familiar with these seven levels means you will almost never need to guess which one to assign.
- Full Control: complete administrative rights over a site; cannot be customised.
- Design: create lists and libraries, edit pages, and apply themes.
- Edit: add, edit and delete lists and list items, including documents.
- Contribute: add, edit and delete items in existing lists and libraries.
- Read: view pages, list items and documents only.
- View Only: restricts downloading for documents with a server-side browser handler; other file types can still be downloaded. It is not a blanket download block.
- Limited Access: automatically applied so a person can reach a specific item without seeing the rest of the site; cannot be customised.
Microsoft documents these seven standard permission levels, noting that Full Control and Limited Access cannot be edited because they underpin how SharePoint works behind the scenes.
Groups sit above these levels. Every modern site gets Owners, Members and Visitors by default, mapping roughly to Full Control, Edit and Read. For a team site built around Microsoft 365, it usually makes sense to manage access through the Microsoft 365 group membership rather than the SharePoint group directly, since that keeps the group consistent across Teams, Outlook and Planner. For a communication site with no underlying Microsoft 365 group, the built-in SharePoint groups are your main tool, and Microsoft’s own guidance backs this split for managing permissions on lists and libraries.
Permission inheritance and unique permissions: why limits matter and how to plan for them
By default, every library, folder and item inherits permissions from the site above it. That single inheritance chain is what keeps a site manageable. The moment you select “Stop Inheriting Permissions” on a folder or item, SharePoint creates a new permission scope with its own access list, separate from everything above it.
Do this a handful of times and it is fine. Do it hundreds of times across a document library and you end up with a sprawl of scopes that is hard to track and slower to process.
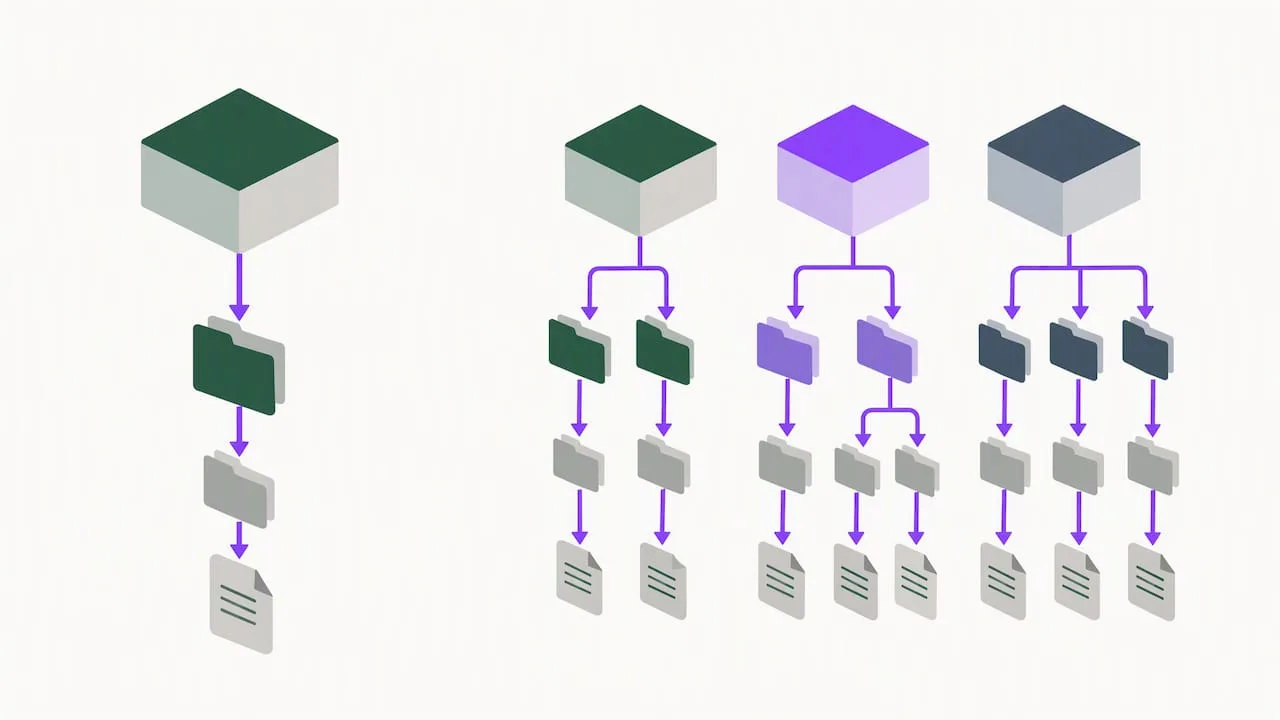
Statistic: SharePoint supports a high number of unique access control lists per list or library, but Microsoft recommends keeping this number quite low for healthy performance, and a folder or list containing many items cannot have its inheritance broken or restored. That ceiling matters more than it first appears, because it quietly rules out ad-hoc permission changes on very large archive libraries.
Three things to plan around:
- Share at folder level wherever possible, since a folder’s permission scope covers everything inside it in one entry rather than many.
- Check how large a library is likely to grow before deciding whether item-level sharing will become unworkable later.
- Time any bulk sharing or migration work before a library crosses the 100,000-item mark, not after.
Step-by-step: grant, change or remove permissions in the SharePoint modern experience
Most permission changes fall into a handful of repeatable tasks. Here is the sequence for each.
To grant site or library access:
- Go to Settings (the gear icon) and select Site permissions.
- Select Advanced permission settings if you need to create a new SharePoint group or review existing ones in detail.
- Choose Grant Permissions, then add the Microsoft 365 group or SharePoint group you want to give access to, selecting “Show options” to pick the exact permission level.
To set unique permissions on a folder or item:
4. Open the library, select the folder or item, and choose Manage access, or go to its detailed permissions page.
5. Select Stop Inheriting Permissions to break the link with the parent, following Microsoft’s own steps for customising site permissions.
6. Choose Grant Permissions and assign the narrowest level that still does the job, such as Read rather than Edit.
To check and share:
7. Use Manage access or Shared with on any file or folder to see who currently has access and adjust or remove it, including setting link expiry where sharing files or folders externally.
8. Use Check Permissions on the site permissions page to confirm exactly what a specific person can do, which is the fastest way to resolve “why can’t they see this” questions.
After any change, sign in as a non-admin test account (or ask a colleague) to confirm access behaves as expected, note whether you have added a new permission scope, and put a reminder in your calendar to review it again next quarter.
Pro Tip: Before breaking inheritance, ask whether a new folder with its own clean permissions would be simpler than carving out an exception inside an existing one.
Permissions strategy and best practices tailored for small businesses
A small team does not need a complicated permissions structure, it needs one that matches how the business actually works. Design your sites and libraries around real access boundaries first (finance, HR, client projects), so permission changes happen rarely rather than constantly.
- Give Edit rights only to the people who genuinely create or amend documents; everyone else gets Read or View Only.
- Avoid “Anyone with the link” sharing for anything sensitive, and default to organisation-only links with an expiry date instead.
- Name every group clearly, such as “Finance Team Edit” rather than “Group 4”, so nobody has to guess its purpose.
- Assign a single owner to each group who is responsible for adding and removing members.
- Write one line describing each group’s purpose somewhere your team can find it, even a shared note.
This approach keeps the number of unique permission scopes low by design rather than by constant tidying later. Microsoft’s own scope guidance makes the same point: structure content around access boundaries and avoid ad-hoc, file-level permission scopes wherever a group-based approach will do.
Pro Tip: When in doubt between two permission levels, choose the lower one. It is far quicker to upgrade someone to Edit than to track down and remove access that should never have been granted.
Audit, review and remediation: a simple recurring process
A short quarterly check keeps permissions from drifting into a mess. Run through this list:
- Count unique permission scopes across your key libraries and flag any sharp increase since the last review.
- List every externally shared link and confirm each one is still needed.
- Review guest accounts and remove any tied to projects that have finished.
- Check the Owners list on every group and site, since ownership tends to go stale as roles change.
Use Check Permissions on individual items when something looks off, and consolidate duplicate groups where you find them. Where a folder no longer needs unique permissions, re-inheriting from the parent is usually the cleanest fix.
When to get help from hostme.ie and what we do
If a permissions audit feels like more than you have time for, or you are planning a migration and want access boundaries mapped out first, that is a typical task handled by IT support providers for Irish sole traders and small businesses. We set up Microsoft 365, review existing permissions, and train staff on managing groups day to day. If you have hit scope or performance limits already, get in touch via WhatsApp for a quick diagnostic conversation.
Author perspective: practical trade-offs and a short checklist
Granular permissions feel safer in the moment, but every unique scope you create is one more thing somebody has to remember and maintain. The businesses that stay out of trouble are the ones that favour groups over exceptions.
A three-line checklist worth running today: use groups instead of individual permissions, avoid file-level sharing for routine work, and put a quarterly review in your calendar now. None of it takes long, and all of it prevents the slow sprawl that makes permissions painful later.
hostme.ie
Quick hostme.ie contact and services links
IT support providers offer hands-on Microsoft 365 and IT support for sole traders and small businesses, including permission reviews and staff training on managing SharePoint access day to day. If you would like a second pair of eyes on your setup, message us on WhatsApp or see our IT support page for more detail.
Sources
- Understanding permission levels in SharePoint – SharePoint in Microsoft 365 | Microsoft Learn
- Customize permissions for a SharePoint list or library | Microsoft Support
FAQ
What are the different SharePoint permissions?
Common SharePoint permission levels include Full Control, Design, Edit, Contribute, Read, View Only and Limited Access, each covering a defined set of actions. Full Control and Limited Access cannot be customised, as Microsoft’s permission levels documentation explains, while the other five can be adjusted to create custom levels if needed.
How do you manage permissions in SharePoint?
Most admins manage permissions through Site permissions and Advanced permission settings, assigning Microsoft 365 groups or SharePoint groups rather than individual users. Microsoft recommends Microsoft 365 Groups for team sites and SharePoint groups for communication sites to keep access consistent and easy to review.
How do I give someone permissions on SharePoint?
Open Site permissions, select the relevant group, and grant them membership, or use “Share” on a specific file or folder to add someone directly with a chosen permission level. For one-off access to a single item, sharing the item directly and setting an expiry date is usually safer than adding them to a broad group.
How do I see what permissions I have in SharePoint?
Check “Shared with” or “Manage access” on any file or folder to see who currently has access and at what level. Site owners and admins can also use “Check Permissions” on the Site permissions page to confirm exactly what a specific person’s effective access is across the site.